
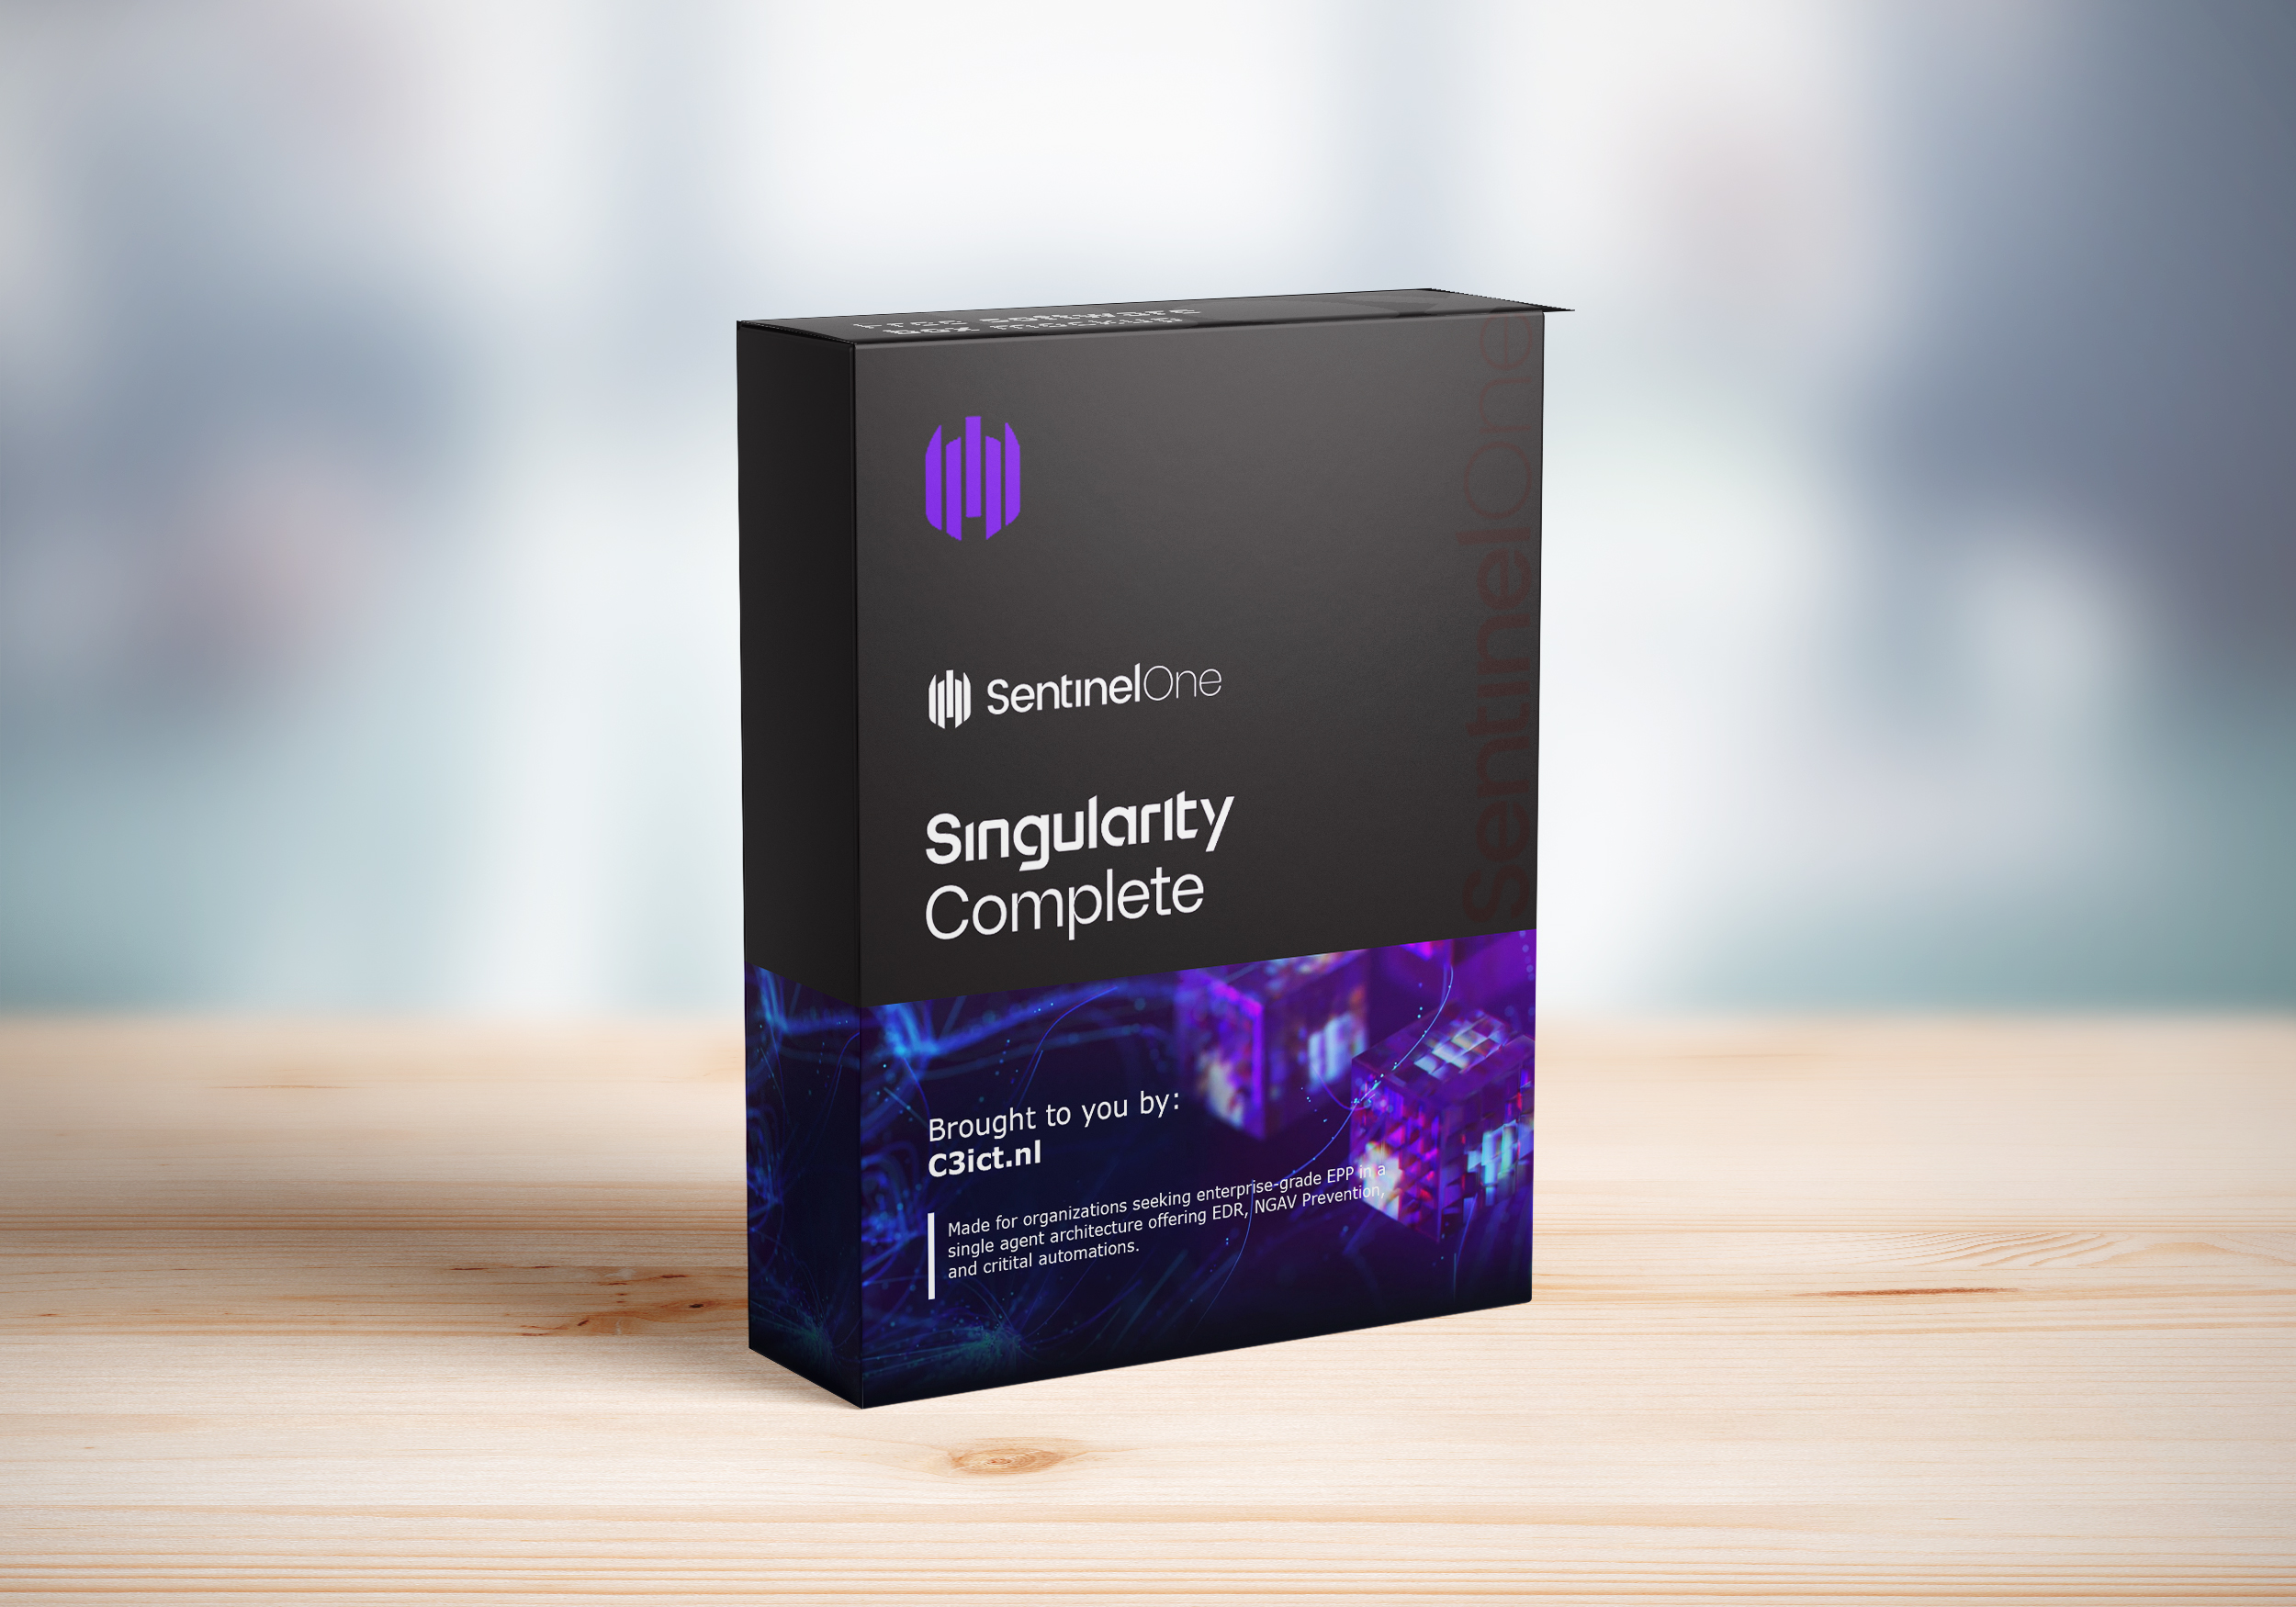

SentinelOne Singularity Complete – 1 year
€90,00 Excl. 21% VAT
SentinelOne Complete adds advanced capabilities such as threat hunting and Deep Visibility. It offers attack prevention and detection across all major vectors, rapid threat elimination with fully automated, policy-based response capabilities, and complete visibility into the endpoint environment with full-context real-time forensics.
SentinelOne Complete includes advanced EDR/Threat Hunting, enabling you to search for attack indicators, investigate existing incidents, perform file integrity monitoring, and eradicate hidden threats. It features an Attack Storyline, a visual diagram representing execution flow, and helps IR teams quickly evaluate the impact of any threat. Advanced capabilities include Deep Visibility in every event on the agent, including the ability to search historical data and gain visibility into encrypted network traffic without pushing certificates or requiring expensive SSL appliances/blades.
In addition, SentinelOne Complete includes Purple AI Foundations as standard, a built-in AI layer that supports your analysts during investigation and response. Instead of manually sifting through raw logs, you get a readable story of what happened, automatically enriched and correlated across all your security data. Purple AI Foundations offers, among other things:
- AI-generated event and alert summaries – complex events are summarized in understandable language, so that analysts understand what is happening more quickly.
- Self-documenting notebooks – investigations are automatically captured in shareable, reusable notebooks, ideal for collaboration and auditing.
- Automatic telemetry correlation – data from endpoints, cloud workloads, and identity sources is brought together into one detailed, visual story of the incident.
- Alert enrichment and triage support – alerts are supplemented with additional context, such as similar alerts and verdicts, to prioritize faster and more specifically.
In this way, Purple AI Foundations helps overburdened security teams understand and handle threats faster, with less manual detective work and shorter response times.
. Minimum order 3 pieces

If you are looking for even more, then Singularity Complete is what you need. Complete is built for enterprises that need modern endpoint protection and Control plus advanced EDR features. Below are the additional features (as well as those from Core & Control) you get with Complete:
-
Patented Storyline™ tech for fast RCA and easy pivots.
-
Integrated ActiveEDR™ visibility to both benign and malicious data.
-
14 - 365+ historical EDR data retention + usable query speeds at scale.
-
Hunt by MITER ATT&CK ® Technique.
-
Mark benign Storylines as threats for enforcement by the EPP function.
-
Automated StorylineTM Active Response (STAR) watchlist functions.
-
Timelines, remote shell, file fetch, sandbox integrations, and more.


You must be logged in to post a comment.