
Serious vulnerability found in the RDS platform
What needs to be done?
C3 ict wishes to urgently inform you about a serious vulnerability in Microsoft's RDS platform. We estimate the potential impact to be very high, hence this direct message. You may have already heard reports, but we would like to provide additional explanation and emphasize the urgency of this update on our part.
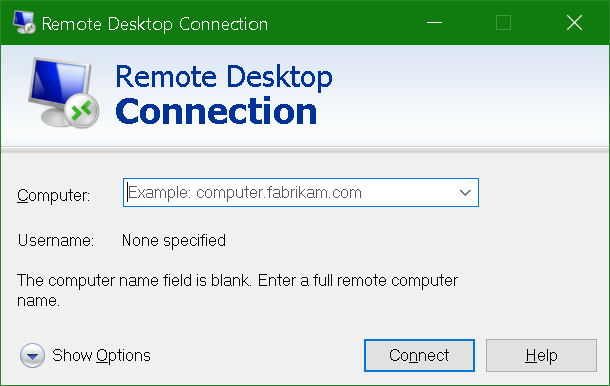
The discovered vulnerability could potentially be exploited by attackers to gain unauthorized access to the system and from there spread further into the network. We would like to highlight the fact that this vulnerability can be exploited automatically and requires no user interaction. This brings to mind a scenario similar to what was seen during the WannaCry attack. The vulnerability impacts the following versions:
• Windows 7
• Windows Server 2008 R2
• Windows Server 2008
• Windows XP
• Windows 2003
Recommended actions:
• Update all systems that could be affected by this vulnerability as soon as possible; this also includes internal systems that are accessible internally via RDP.
• Enable access via RDP with 2-factor authentication (we can set this up for you)
• Updates on outdated operating systems must always be applied manually
General recommendations:
• C3ict advises against making RDP accessible directly via the internet
• It is advisable to secure RDP with 2-factor authentication
• Critically review your password policy and encourage the use of long, unique passwords
• Update operating systems and other software as soon as possible
• Install our Eset Endpoint & Server Security within the network.
Request a quote?
Would you like a quote for 2-factor security for your server, or do you want to purchase Eset antivirus software? Then please contact us.


You must be logged in to post a comment.